CVE-2024-26152
4.7 · MEDIUMOverview
CVE-2024-26152 is a medium-severity vulnerability affecting humansignal label_studio. It was published on February 22, 2024 and has a CVSS 3.1 base score of 4.7 (MEDIUM).
This vulnerability has a CVSS 3.1 base score of 4.7, rated MEDIUM. It can be exploited remotely over the network. No authentication or special privileges are required for exploitation.
Technical Description
### Summary
On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.
### Details
Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.
### PoC
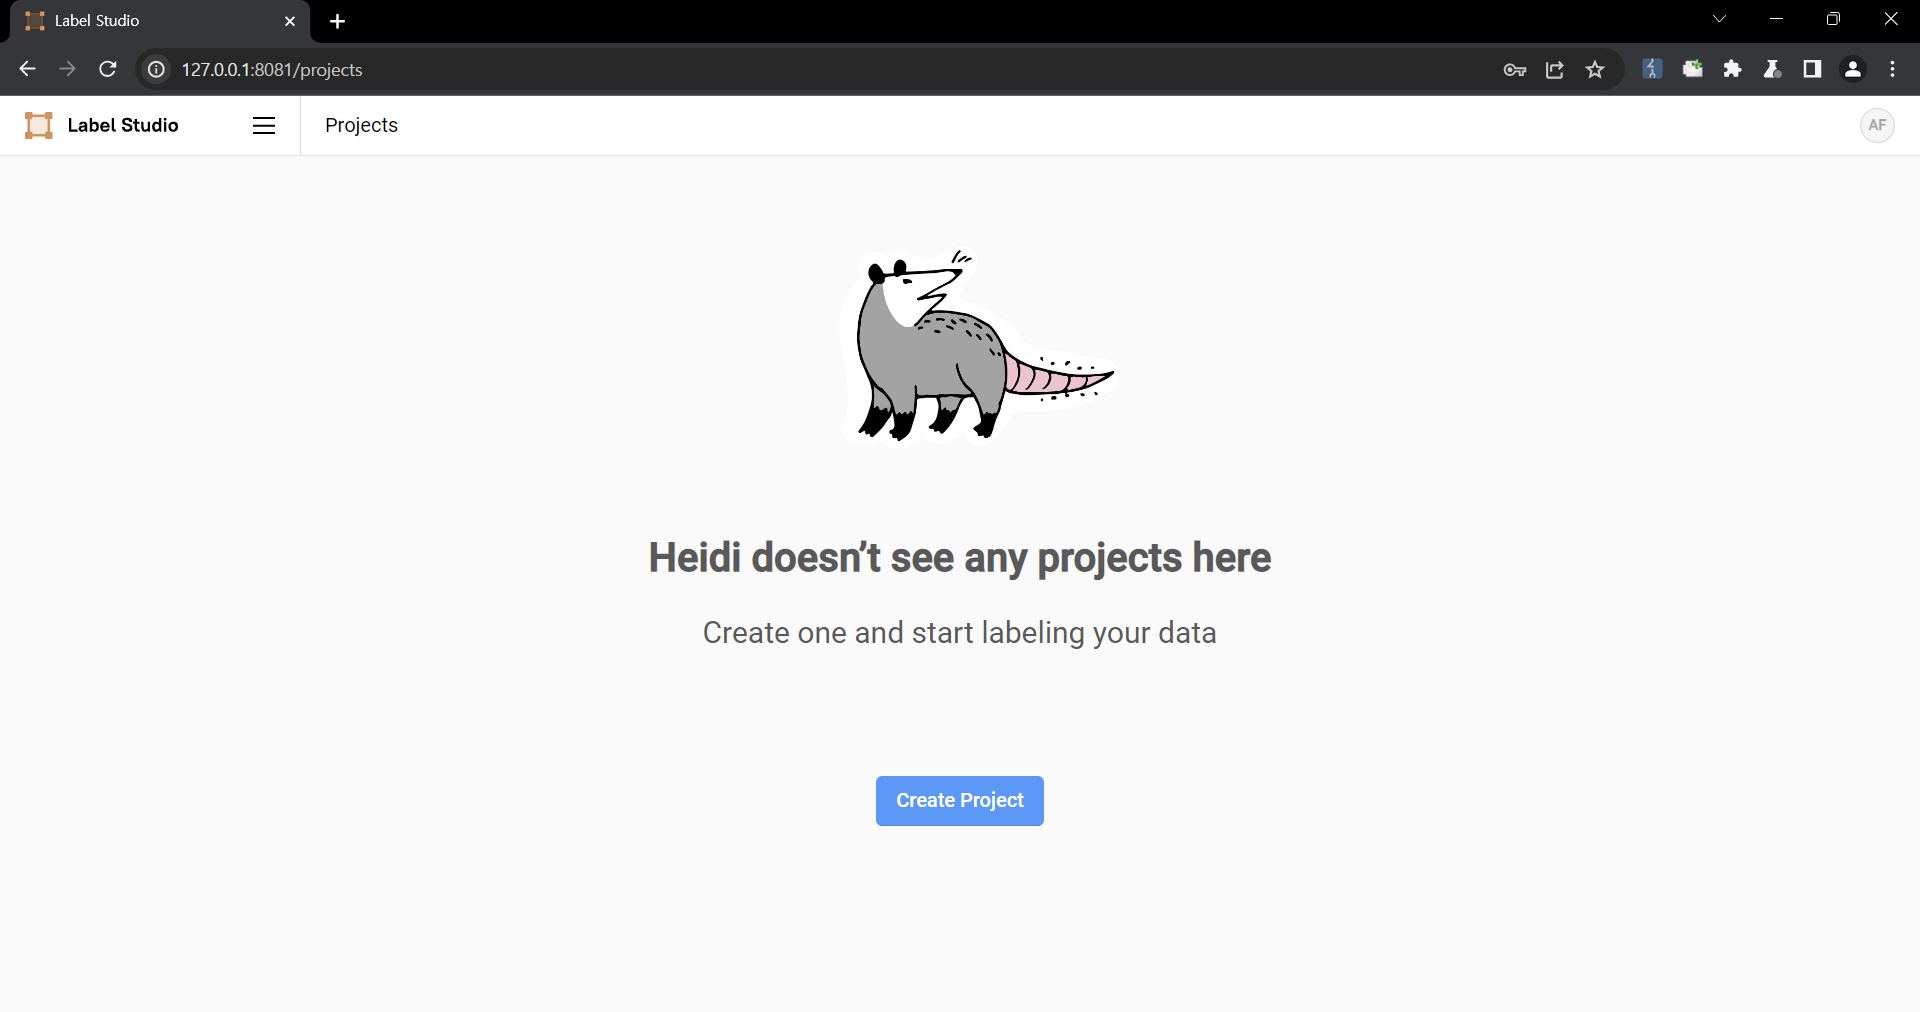
1. Create a project.
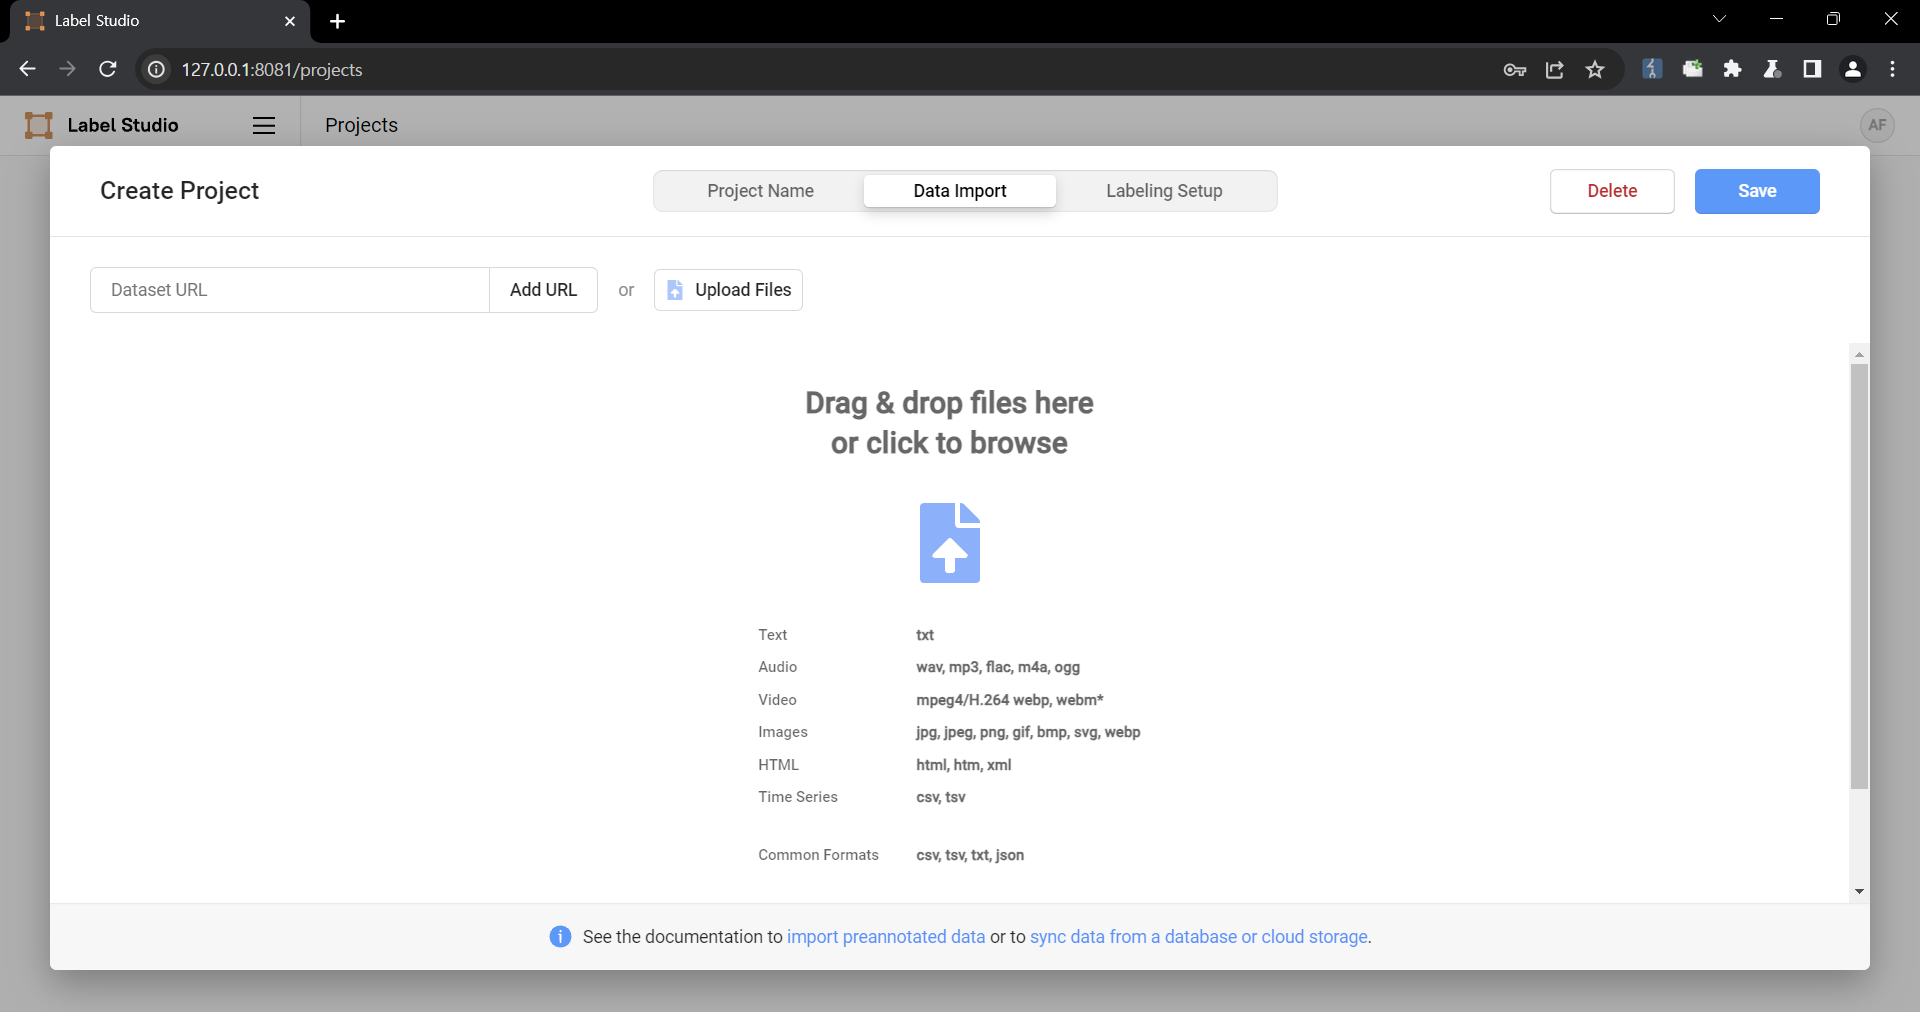
2. Upload a file containing the payload using the "Upload Files" function.
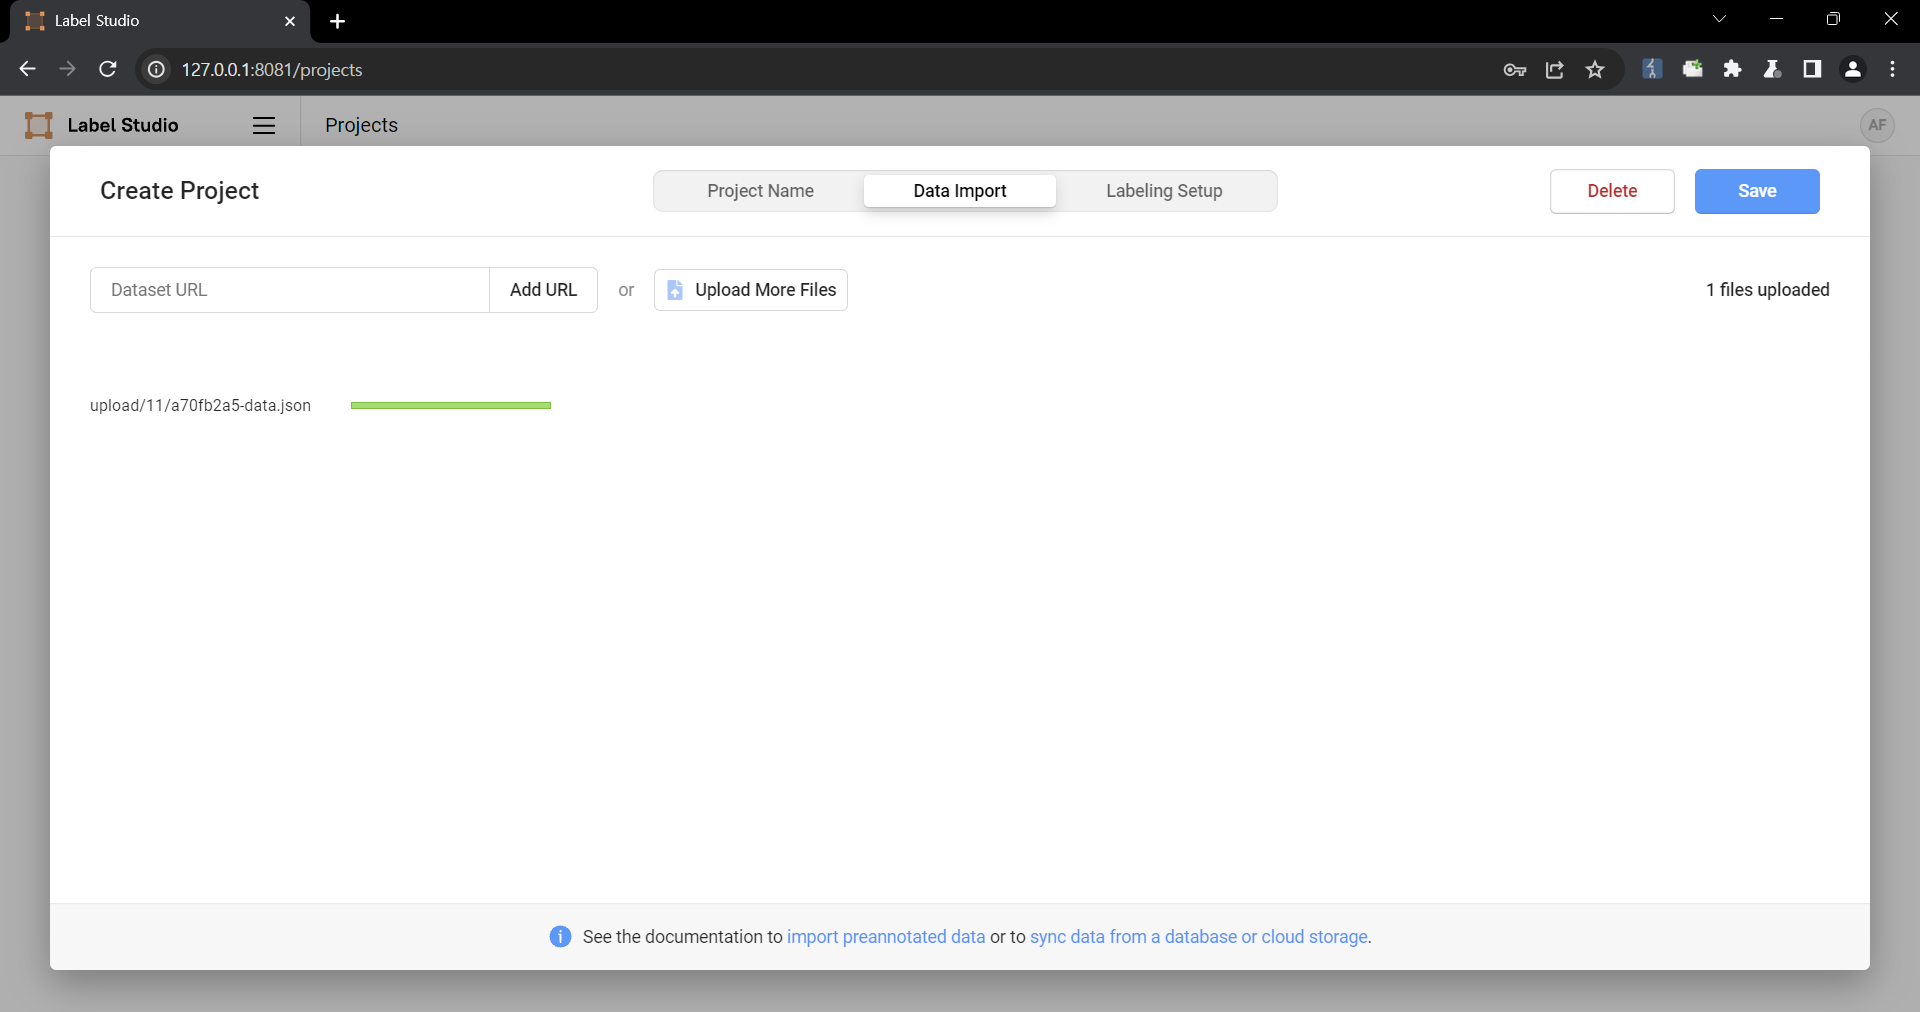
The following are the contents of the files used in the PoC
```
{
"data": {
"prompt": "
Remediation
Check the references section for vendor advisories and patches from humansignal. Update label_studio to the latest patched version. If immediate patching is not possible, review the CVSS vector to understand the attack surface and apply compensating controls such as network segmentation or access restrictions.
Affected Products
| Vendor | Product | Versions | Status |
|---|---|---|---|
| humansignal | label_studio | >= 0, < 1.11.0 | Affected |
References
Frequently Asked Questions
What is CVE-2024-26152?
CVE-2024-26152 is a medium-severity vulnerability affecting humansignal label_studio. It was published on February 22, 2024 and has a CVSS 3.1 base score of 4.7 (MEDIUM).
How severe is CVE-2024-26152?
This vulnerability has a CVSS 3.1 base score of 4.7, rated MEDIUM. It can be exploited remotely over the network. No authentication or special privileges are required for exploitation.
How do I fix or remediate CVE-2024-26152?
Check the references section for vendor advisories and patches from humansignal. Update label_studio to the latest patched version. If immediate patching is not possible, review the CVSS vector to understand the attack surface and apply compensating controls such as network segmentation or access restrictions.
How can CyberStrike help with CVE-2024-26152?
CyberStrike's AI-powered security agents can automatically detect CVE-2024-26152 across your infrastructure using autonomous pentesting, DAST scanning, and HackBrowser. The platform continuously monitors for known vulnerabilities and provides actionable remediation guidance prioritized by real-world exploitability.
How CyberStrike Helps
AI agents map your attack surface to find vulnerabilities like this one.
Automated penetration testing that runs continuously, not just quarterly.
AI-driven PR review catches vulnerable dependencies before they ship.
Browser-based exploitation validates findings with real proof-of-concept.
Related MEDIUM CVEs from 2024
View all →OCSInventory allow stored email template with special characters that lead to a Stored cross-site Sc
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation
This vulnerability exist in Skyworth Router CM5100, version 4.1.1.24, due to insufficient validation